Deploy with regional truth, local control, and accountable evidence
Define scope, verify current operability, and configure jurisdiction, data, time, locale, identity, policy, integrations, support, and rollout evidence before activation.
Availability is confirmed against current technical, contractual, documentation, monitoring, support, legal, and commercial readiness — not against a coverage map.
Above-the-fold boundary
This page governs deployment readiness. It is not a coverage promise, a compliance guarantee, or a global HR product. No map pins, flags, badge walls, or implied availability appear anywhere on it — by design.
Deployment Readiness
Six Dimensions Verified Before Activation
Each dimension carries its own status, owner, evidence, and review date. None of them is inferred from another, and there is no combined readiness percentage.


Regional operability
Technical, contractual, legal, documentation, monitoring, support, and commercial readiness.
View verification method
Local configuration
Jurisdiction, time zone, DST, locale, policy, notice, consultation, retention.
View configuration model
Identity and integrations
Authorized access, mapping, validation, acknowledgement, reconciliation, corrections.
Review connection readiness
Support and continuity
Support profile, incident route, status, continuity, rollback, ownership.
Review operating readiness
Evidence and approval
Tests, gaps, named review, decision, effective date, history.
View evidence modelWhy Global Deployment Requires Control
Five Ways Uncontrolled Rollout Damages the Record
Deployment across boundaries is a governed operating problem, not a feature list. Each risk below has a specific control on this page.
Different legal and operating contexts
Risk: policy drift, unclear ownership, and inconsistent notice, correction, approval, and record treatment.
Page response — scope model, jurisdiction profiles, inheritance, exceptions, named owners, evidence.
Time behaves differently by location
Risk: DST, calendars, overnight shifts, cutover, historical rule changes, and period boundaries can distort records.
Page response — versioned time and locale controls, scenario tests, neutral conflict states, recalculation evidence.
Data and support claims collapse together
Risk: deployment, data location, transfers, support, legal review, and commercial status get treated as one fact.
Page response — separate registries with their own statuses, owners, dates, limitations, and authoritative routes.
Activation precedes readiness
Risk: identity, mapping, communication, support, correction, and rollback gaps surface after launch.
Page response — readiness test suite, named approval, waves, rollback, post-launch review.
Workers experience local consequences
Risk: incorrect context and unclear rights reduce trust and create record disputes.
Page response — notice, visibility, correction, human review, consultation, accessible support.
Governed Deployment Lifecycle
Nine Stages, in Order, With Activation Blocked Until Approval
Each stage states what your organization sees and what the platform does. Nothing auto-advances, and no stage can be skipped by configuration.
Stage 01
Establish scope
You see
Entities, locations, groups, owners, timeline, policies, systems, support.
Platform does
Creates a versioned deployment charter.
Stage 02
Verify operability
You see
Current readiness and its stated limitations.
Platform does
Checks approved technical, contractual, legal, support, documentation, monitoring, and commercial records.
Stage 03
Configure local context
You see
Jurisdiction, time, locale, calendar, policies, notices, retention.
Platform does
Applies supported profiles, inheritance, impact and conflict checks.
Stage 04
Connect and map
You see
Identity, integrations, inputs, outputs, corrections.
Platform does
Enforces authorization, mapping, validation, acknowledgement, reconciliation.
Stage 05
Test readiness
You see
Scenarios, permissions, failures, support, accessibility, rollback.
Platform does
Runs the defined test suites and records every result.
Stage 06
Approve the wave
You see
Reviewers, evidence, gaps, cutover, rollback.
Platform does
Blocks activation until required decisions are complete.
Stage 07
Activate
You see
Approved scope and effective time.
Platform does
Activates only authorized scope and records the event.
Stage 08
Observe and reconcile
You see
Quality, support, incidents, acknowledgements, corrections.
Platform does
Routes accountable attention using neutral states.
Stage 09
Stabilize, expand, suspend, or retire
You see
Post-launch review and future scope.
Platform does
Versions each change and preserves withdrawal evidence.

System readiness supports review. Authorized people approve consequential deployment and workforce-record decisions.
Organizational Scope & Entity Model
Deployment Scope Is a Governed Object, Not an Inferred Org Chart
Model organization, legal entity, business unit, region, location, department, team, and workforce group relationships explicitly — then assign an owner to each one.
Ownership
- Deployment and entity owners
- Location and policy owners
- Identity, integration, support owners
- Privacy, legal, worker-communication owners
Lifecycle states
- Draft · review · approved
- Active · suspended
- Closing · archived · withdrawn
- Each with an effective date and evidence
Boundaries
- Included and excluded populations
- Work patterns and locations
- Systems, outputs, data profiles
- Named support contacts
Impact preview
- Affected policies and identities
- Integrations and reports
- Notices, approvals, workers
- Evidence references
No inference
Entity or address data never automatically determines law, policy, data location, or commercial availability. Someone authorized decides, and the decision is recorded.
Regional Availability & Commercial Eligibility
We Publish the Verification Method, Not a Country List
Six dimensions are assessed separately for your intended deployment scope. A passing technical status does not make a region available, and interest, locale, or IP address never implies commercial eligibility.
- Technical — services, dependencies, observability, continuity, release readiness
- Contractual — contracting authority, terms, DPA, order form, entitlements
- Legal and privacy — approved review for the current service and data model
- Documentation — product, data-flow, configuration, support, limitation docs
- Monitoring and operations — health, alerts, incident ownership, change control
- Commercial — entitlement, sales ownership, capacity, launch terms
No speculative availability is shown. If a location has not been assessed, the answer is “not assessed” with a named owner and a route to a verified response.
Readiness summary — counts, not a score
| Scope | Technical | Contractual | Legal | Support | Publishability |
|---|---|---|---|---|---|
| Scope A | Operational | Approved | Reviewed | Covered | Public eligible |
| Scope B | Operational | Under review | Under review | Evidence missing | Controlled response |
| Scope C | Pilot restricted | Not assessed | Not assessed | Not assessed | Internal only |
| Scope D | Suspended | Approved | Under review | Withdrawn | Withdraw immediately |
Availability registry, synthetic. Each dimension carries its own evidence reference, owner, last-verified and next-review date.
A passing internal status never publishes a regional claim automatically. Content, legal, product, support, commercial, accessibility, analytics, route, and QA approvals all remain required.
Data Location, Residency & Transfers
Data Location Is a Governed Profile, Not a Flag on a Map
Identity, workforce record, configuration, evidence, support, telemetry, export, backup, and integration data may be handled differently. Each category resolves to an approved profile with a purpose, an authority, and a review date.
| Concept | Public treatment | Product proof |
|---|---|---|
| Data categories | Categories are named separately; they do not share one location fact. | Category-to-location register with purpose and authority. |
| Primary processing / storage | Only approved options and their boundaries are described. | Profile, evidence, owner, effective and review dates. |
| Backup / continuity | Operational copies are separate from the primary location. | Location class, retention, access controls, restoration test. |
| Transfers | Transfer paths and mechanisms depend on scope and terms. | Source, destination, purpose, mechanism reference, approver, status. |
| Subprocessors / infrastructure | Routes to the current authoritative list and data map. | Artifact status, version, owner, review date. |
| Support access | Data location is separate from authorized support access. | Role, purpose, restriction, expiry, evidence. |
| Relocation | Requires impact assessment, notices or terms, test, cutover, rollback. | Versioned change plan. No silent relocation. |
Jurisdiction & Legal Configuration
Jurisdiction-Aware Configuration, With Limits Stated
A governed workflow — not a compliance engine. Every profile has an owner, a source, a version, an effective date, a review cadence, and written limitations.
Jurisdiction profile
Approved inputs, owner, source, version, effective date, review cadence, and stated limitations.
Applicability review
Authorized reviewers decide whether a profile applies to an entity, location, group, or work pattern.
Policy mapping
Time, attendance, break and rest, approval, correction, retention, evidence, and communication policies.
Local exceptions
Reason category, scope, owner, reviewer and approver, effective and expiry dates, impact, evidence.
Conflict handling
Neutral conflict state, activation blocked where required. The platform never selects a “more compliant” value on its own.
Change control
Version, compare, approve, schedule, communicate, roll back, and preserve historical applicability.
Time Zones, DST & Calendar Integrity
Time Context Is a Record-Integrity Control
Time is where distributed workforce records quietly break. Every zone, transition, and calendar convention is versioned, tested, and explicitly owned.
Authoritative zone — approved identifier, scope, source, version. Human labels and offsets are contextual only.
DST transitions — spring-forward, fall-back, non-hour changes, ambiguous and skipped local times, overnight shifts, historical rule changes.
Reference contexts — worker, location, organization, policy, integration, export, and report precedence, with differences shown.
Cutover — activation instant, local interpretation, period boundary, historical records, rollback.
Calendar and workweek — versioned week start, holidays, working days, local date, period boundary, exception ownership.
Exports — carry timestamp, time-zone context, mapping version, and acknowledgement per the approved contract.
Corrections — preserve original and corrected values, reason, authority, affected outputs, recalculation, evidence.
Test gate
No rollout wave passes readiness until the approved time and DST scenario suite succeeds — or until every exception is explicitly documented, owned, accepted, and visible.
Localization, Language & Locale
Localization Is Product, Content, Accessibility, and Support Work
Machine translation alone is not localization. Language packs release only with an owner, a version, a review date, a fallback, and quality evidence.
Language
Approved packs only, each with owner, version, review date, fallback, and quality evidence.
Dates, numbers, time
Locale-aware display with unambiguous operational and export formats. Governed values never change.
Calendars and week conventions
Display convention stays distinct from policy and period boundaries.
Terminology
A controlled glossary for workers, roles, states, rights, evidence, and actions.
Legal and worker copy
Authoritative localized notices and contractual text stay separate from interface translation.
Accessibility per locale
Labels, focus, text expansion, reflow, input methods, captions, contrast, and errors are verified.
Fallback
Languages never mix unpredictably. The current fallback is visible and can be changed with approval.
Support boundary
A translated interface does not imply support coverage in that language. Those are separate registries.
Policy Inheritance & Local Exceptions
Global Consistency and Local Control, Made Explicit
Inheritance and exception logic are visible, so you can always see which rule applies and why — before activation, not after a dispute.
| Pattern | Required behavior | Risk prevented |
|---|---|---|
| Organization default | Approved baseline with broad scope, owner, version, effective date, review. | Unowned configuration |
| Entity / regional override | Allowed only where role, capability, jurisdiction review, and approval permit. | Silent fragmentation |
| Local exception | Reason, scope, expiry, impact, communication, approval, evidence. | Permanent workaround |
| Precedence | Shows which rule applies and why; surfaces conflicts before activation. | Ambiguous classification |
| Propagation | Previews affected records, integrations, reports, notices, and waves. | Unexpected downstream impact |
| Worker visibility | Shows applicable context, effective date, correction route, authorized explanation. | Opaque outcomes |
| Rollback | Restores the approved prior version without deleting the attempted change or its evidence. | Loss of accountability |
Identity & Access Across Boundaries
Failure Never Broadens Access
Every account and service identity resolves to an approved organization and lifecycle authority. Location is never used to guess who someone is or what they may do.
Identity & AccessRole scope
Global, entity, regional, location, deployment, policy, identity, integration, support, legal and privacy, auditor, viewer.
Least privilege
Temporary and emergency access carries purpose, scope, approver, expiry, review, revocation, and evidence.
Separation of duties
No single role defines scope, approves legal and data readiness, activates rollout, and closes evidence where separation is required.
Access review
Privileged, cross-entity, regional, support, export, and service-identity access is reviewed before and after rollout.
Failure behavior
Authentication or authorization failure does not broaden access or bypass approval. There is no privilege fallback.
Evidence
Actor, role, scope, action, object, timestamp, result, reason category, and references — subject to data minimization.
Integration & Data-Flow Readiness
Connections Are Governed, Not Browsed From a Marketplace
Each authorized flow states its system authority, purpose, direction, identity, scope, owner, and current support status. There is no provider list and no implied catalogue.
01 · Authorize
Source and destination
System and object authority, purpose, direction, identity, scope, owner, support status.
02 · Map
Versioned mapping
Fields, time and locale, units, enumerations, validation, null and conflict behavior, limitations.
03 · Test
Isolated environment
Approved non-production scope, synthetic data, test identity, isolation, cleanup, evidence.
04 · Reconcile
Acknowledge and correct
Delivery and receipt, retry, idempotency, ordering, duplicate detection, mismatch resolution.
Required behavior
 Correction propagation to every affected destination, with recalculation and acknowledgement
- Cutover with queue handling, parallel validation, rollback, recovery, and communication
- Failure states that stay visible, neutral, and owned
- Evidence preserved for each run, retry, and reconciliation

Never permitted
 Guessing a value when data is missing, late, or conflicting
- Privilege expansion to complete a flow
- Silent drops or duplicate acceptance
- Irreversible partial activation
- Treating an integration as proof of an approved data-location or regional profile
Data Migration Boundary
Deployment Can Identify Migration Dependencies. It Cannot Deliver Them.
Migration readiness may block a wave. That is different from offering a migration service, and this page does not offer one.
What deployment covers
- Imported records require scope, format, mapping, validation, correction, reconciliation, cutover, rollback, ownership, privacy, and evidence
- Historical time, locale, DST, policy, identity, and entity context must remain interpretable
- Migration is recorded as required, not required, under review, blocked, or separately scoped
- A wave can be blocked until migration evidence and acceptance are complete
What this page never claims
- A released migration service, supported formats, volumes, timelines, pricing, or staffing
- Data cleansing guarantees or named legacy systems
- Automatic reconstruction of missing historical context or legal applicability
- A “migrate now” action before the dedicated offer is approved
- That activation validates migrated records
Sequence boundary
Implementation Services and Data Migration remain separately gated and are absent as released offers until their own scope, capacity, entitlement, legal, documentation, support, and QA gates pass.
Rollout Waves, Pilot & Cutover
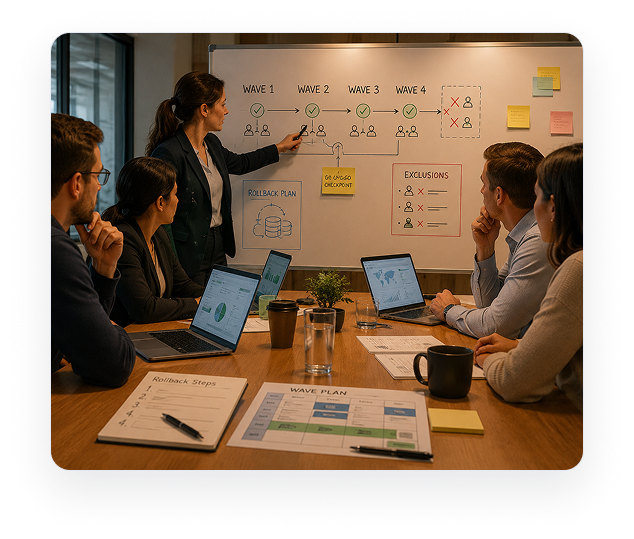
Approved Waves, Explicit Exclusions, Real Rollback
Every wave names what is in scope and what is deliberately out of it. Entry criteria are checked, not assumed, and rollback is designed before activation rather than after an incident.
Wave record
- Name, purpose, owner, status, version
- Entities, locations, groups, roles
- Policies, integrations, outputs
- Data and support profiles
Entry criteria
- Availability, identity, policy
- Time and locale test results
- Integrations, notices, consultation
- Training dependency, support, evidence
Cutover
- Date, time, and zone
- Sequence, dependencies, any freeze
- Responsible roles and communication
- Monitoring during the window
Rollback
- Trigger and authority
- Steps, data and integration handling
- Communication plan
- Recovery validation
Operational Monitoring & Reconciliation
We Monitor the System, Never the Person
Monitoring covers service, record, integration, support, and evidence quality. It never covers covert behavior or individual productivity — and no configuration changes that.
| Monitor | Approved signals | Action model |
|---|---|---|
| Configuration | Unexpected version, missing owner, expired exception, unreviewed change | Accountable attention with owner, due state, evidence, neutral language |
| Time / locale | DST mismatch, ambiguous time, calendar conflict, format failure | Block or review — never a guessed resolution |
| Identity / access | Provisioning mismatch, expired privilege, denied action, overdue review | Least-privilege recovery, no broader fallback |
| Integrations | Failure, duplicate, ordering, mapping, acknowledgement, correction pending | Retry safely, reconcile, preserve evidence |
| Support / incidents | Routing gap, unacknowledged case, owner mismatch, overdue update | Escalate by approved support profile |
| Evidence / documents | Stale artifact, missing review, withdrawn link, incomplete approval, export failure | Withdraw the claim and route accountable review |
Never collected or represented
- Screenshots
- Keystroke content
- URL history
- Application-name monitoring
- Clipboard collection
- Hidden productivity scores
Human authority holds
- Flags and anomalies are evidence for review, not findings
- Time classification is deterministic, policy-bound, and explainable
- Kairos may retrieve, summarize, and explain approved governed data — Kairos decides nothing
- Authorized people make every consequential decision
Support Coverage & Incident Routing
Support Readiness Is a Deployment Control, Not a Slogan
A support profile is a contractual boundary with channels, a coverage window, a time zone, a language, an entitlement, severity definitions, response authority, exclusions, an owner, and a review date.
Local ownership
Your named contacts for administration, identity, policy, legal and privacy, integrations, finance and payroll, worker communication, and continuity.
Incident route
Detection source, severity, owner, escalation, status communication, customer action, evidence, closure review.
Regional handoff
Only where current and supported. Context, ownership, access, acknowledgement, and evidence are preserved across the handoff.
System status
Operational incidents route to the authoritative status surface. Marketing pages never duplicate live state.
Existing customers
Account-aware support and status, with no new lead form in the way.
Language we do not use
- 24/7, follow-the-sun, or global support
- Local, dedicated, or premium coverage
- Guaranteed response without current terms
Reliability, Continuity & Disaster Recovery
The Governance Model, Without Invented Numbers
Resilience claims resolve to approved authority and your correct entitlement. Marketing does not derive, round, or restate them.
| Area | Required specification | Claim boundary |
|---|---|---|
| Dependency map | Approved service, identity, integration, data, support, and external dependencies. | No “fully redundant” claim without evidence. |
| Continuity mode | Supported degraded behavior, read and write boundaries, communication, queueing, recovery, evidence. | No invented offline or regional failover. |
| Backup and restore | Approved scope, retention, access, validation, restoration test, owner, evidence. | No location or recovery guarantee without documentation. |
| Failover and relocation | Preconditions, authority, data and access impact, integrations, support, communication, test, rollback. | No active-active, multi-region, or automatic claim without proof. |
| RTO / RPO / SLO / SLA | Only from approved authority and the correct entitlement. | Values are never derived or rounded for marketing. |
| Post-incident | Timeline, impact, actions, evidence, communication, follow-up ownership. | No blame labels and no hidden findings. |
Worker Visibility, Correction & Consultation
A Deployment Is Not Ready If Workers Cannot Understand or Correct the Record
Local context changes what a record means. Notice, visibility, correction, and human review are readiness criteria on this page, not a trust-page afterthought.
Notice and explanation
Accessible information about data categories, purposes, sources, rules, time and locale context, retention, access, corrections, and escalation.
Record visibility
Supported records, states, effective context, approvals, corrections, and outcomes — subject to approved access.
Correction
Issue, reason and evidence where appropriate, a neutral pending state, human review, outcome, and downstream propagation.
Human review
Consequential decisions stay with authorized people. Anomalies are not misconduct findings.
Consultation and representation
Required materials, ownership, status, evidence, and unresolved obligations are recorded where applicable.
No retaliation inference
Risk is never inferred or scored from a worker's use of correction, support, accessibility, or representation.
Security, Privacy & Trust Routing
Every Claim Resolves to an Authoritative Surface
This page summarizes deployment implications and then hands you to the surface that owns the evidence.
| Topic | Deployment treatment | Authoritative route |
|---|---|---|
| Security | Least privilege, change control, evidence, incident routing, support access, current limitations. | Security |
| Privacy | Minimization, data categories, location and transfer, retention, rights, current terms. | Privacy & DPA |
| Anti-surveillance | The exact invariant, across every tier and configuration. | Anti-Surveillance |
| Human control | Named approval, neutral states, correction, escalation. | Human-in-Command |
| AI governance | Deterministic classification, approved AI scope only, Kairos decides nothing. | AI Governance |
| Accessibility | WCAG 2.2 AA is release-blocking. Known limitations and remediation are published. | Accessibility |
| Reliability and incidents | Operational status and communications. | System Status |
| Procurement | Current artifacts with status, owner, review date, and withdrawal handling. | Procurement & Legal |
Evidence, Procurement & Commercial Readiness
Four Records That Make a Deployment Defensible
Evidence supports deployment, procurement, operations, and review — without exposing sensitive worker, security, legal, credential, or contract detail.
Record 01
Deployment charter
Scope, purpose, owners, included and excluded objects, timeline, dependencies, status, version.
Closes with
Named approval.
Record 02
Availability record
Scope, dimensions, status, evidence references, owner, reviewer, limitations.
Closes with
Effective and review dates.
Record 03
Configuration and test
Profiles, changes, impact, expected and actual results, defects, reviewer and approver.
Closes with
Effective date.
Record 04
Rollout decision
Wave, evidence summary, unresolved conditions, approvers, decision, cutover and rollback, communication.
Closes with
Recorded activation event.
Deployment Questions Answered
Six Answers, No Overclaim
A governed process for scope, operability, local configuration, tests, approval, activation, and evidence. It is how a deployment becomes defensible before it becomes live.