Evidence before
assertion.
Trust in how we
operate.
ZoikoTime is built for human authority, privacy, and operational truth. Explore our commitments, controls, policies, and operational assurance—verified, current, and transparently maintained.
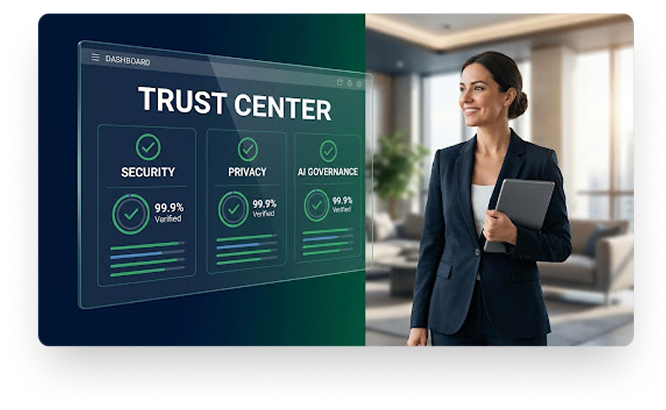
Trust at every layer
Our commitments are embedded across product, people, and operations.
Human-in- Command
Human review remains authoritative for consequential decisions.
Privacy by Design
Data minimization, purpose limitation, and strong default protections.
Deterministic Classification
No automated decision-making. ML used only for anomaly functions.
Transparency
We explain what we do, how we do it, and how we're held accountable.
Accountability
Named ownership, real reviews, and correction pathways.
Our Anti-Surveillance
Commitment
ZoikoTime does not sell, rent, trade, or share personal data. We do not track you across websites or applications. We do not use dark patterns or manipulate choices. You are not profiled. You are not scored. You are not surveilled.
Trust Center
Core trust destinations available now. Each page is owned, dated, and evidentiary.
How we operate
Principles that guide our decisions and daily operations. These aren't just words; they are built into the architecture of our business.

Purpose Limitation
We use data only for stated, legitimate purposes clearly defined in our agreements.

Data Minimization
We collect the minimum data necessary for operations, avoiding toxic data lakes.

Evidence First
Every claim is backed by telemetry, logs, or external audits—never just a handshake.
100% Audit Readiness
Continuous monitoring enabled
Resources & compliance
Trust Policies Library
Access all external-facing legal and trust policies.
Regulatory Mappings
See how we map to GDPR, CCPA, and global frameworks.

Certifications
Download ISO, SOC2, and other trust certifications.

Need access to additional evidence?
Qualified organizations can request access to controlled evidence rooms, security reviews, and procurement documentation for deeper diligence.